Posts

Showing posts with the label openpacket

New Online Packet Repository

Image
As of a few weeks ago I am no longer involved with OpenPacket.org. One of the reasons is a great new online packet repository sponsored and run by Mu Dynamics called Pcapr . I've had an account there for a few months, but it looks like the site is now open to the general public. Check it out -- there's a lot of cool features already. Richard Bejtlich is teaching new classes in DC and Europe in 2009. Register by 1 Jan and 1 Feb, respectively, for the best rates.

Bejtlich Keynote at 1st ACM Workshop on Network Data Anonymization

Image
Brian Trammell and Bill Yurcik were kind enough to ask me to deliver the keynote at the 1st ACM Workshop on Network Data Anonymization (NDA 2008). The one day event takes place 31 October 2008 at George Mason University in northern VA. My talk will discuss the trials and tribulations of OpenPacket.org , and changes planned for the project.

Packet Anonymization with PktAnon

Image
I noticed a new tool on Packetstorm recently: PktAnon by Christoph P. Mayer, Thomas Gamer, and Dr. Marcus Schöller. This tool seems powerful because you can apply a variety of anonymization policies based on settings you apply in an XML configuration file. It was easy to install the tool on Debian 4.0: tws:~# cd /usr/local/src tws:/usr/local/src# wget http://www.tm.uka.de/pktanon/download/pktanon-1.2.0-dev .tar.gz ...edited... tws:/usr/local/src# tar -xzf pktanon-1.2.0-dev.tar.gz tws:/usr/local/src# http://www.tm.uka.de/pktanon/download/pktanon-1.2.0-dev.tar. gz tws:/usr/local/src# sudo apt-get install libxerces27-dev libboost-dev -su: sudo: command not found tws:/usr/local/src# apt-get install libxerces27-dev libboost-dev Reading package lists... Done Building dependency tree... Done The...

OpenPacket.org 1.0 Is Live

Image
Nearly three years after the initial post describing the idea , I am happy to report that OpenPacket.org 1.0 is ready for public use, free of charge. The mission of OpenPacket.org is to provide quality network traffic traces to researchers, analysts, and other members of the digital security community. One of the most difficult problems facing researchers, analysts, and others is understanding traffic carried by networks. At present there is no central repository of traces from which a student of network traffic could draw samples. OpenPacket.org will provide one possible solution to this problem. Analysts looking for network traffic of a particular type can visit OpenPacket.org, query the OpenPacket.org capture repo for matching traces, and download those packets in their original format (e.g., Libpcap, etc.). The analyst will be able to process and analyze that traffic using tools of their choice, like Tcpdump, Snort, Ethereal, and so on. Analysts who collect their own traffic wil...

OpenPacket.org Developments

Image
I am happy to report that work on OpenPacket.org is back on track, thanks to a new volunteer Web application developer. Please read the rest of the story at the Openpacket.org Blog .

OpenPacket.org Update

Image
I just posted news on OpenPacket.org at the OpenPacket Blog . I made an initial announcement about OpenPacket last year . In short, this project is going nowhere unless I get some help with development or financing, due to my lack of Web development skill and time. I appreciate any comments you might post on the OpenPacket Blog . Update: Please visit the OpenPacket Blog for fresh updates. I created devel and users mailing lists, and two people have already volunteered development help. Wow!

Snort.org Posts BlackWorm Packet Captures

The folks at Sourcefire have done the analyst community a great service by posting traffic captures of CME-24 , aka "BlackWorm". Kudos also to the Common Malware Enumeration project for providing an easy way to reference malware! Once OpenPacket.org gets going, I hope to host these sorts of captures there. Update : Check out this Sourcefire VRT analysis .

Thank You for Another Great Year

Image
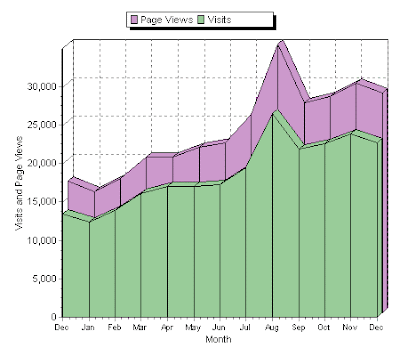
Exactly one year ago today I posted a thank-you note for the great year of blogging in 2004. A look at the 2004 statistics shows as recently as July 2004, this blog had less than 6,000 visitors per month, as tracked by Sitemeter . I have no idea how Atom, RSS, and other republishing is affects those statistics. Soon after my first book was published, we broke through the 10,000 per month mark and have never looked back. As you can see from the 2005 chart above, we're at the 22,000 per month mark now, and broke through 25,000 in August during my coverage of Ciscogate . This blog continues to be a nonpaying venture, despite offers to commercialize, syndicate and repackage the content elsewhere. Others already do this without my permission, but I thank those more responsible people who ask before posting my content elsewhere. For example, I've given the great publisher Apress blanket permission to quote anything I say here. This is my small way to say thank you for th...

Marcus Sachs in SC Magazine

I was pleased to hear what Marcus Sachs is working on, courtesy of an interview by Illena Armstrong and Marcia Savage in this month's SC Magazine . I first met Marcus when I was an Air Force captain at the AFCERT and he was an Army Major at the JTF-CND. Marcus mentioned a project that caught my attention: "We're also building a database of large data sets collected from the internet. The intent is to help researchers who might be working on a new security device. Rather than trying to connect to their own networks and pull live data in from their university network, or wherever they are doing the research, we want to provide them with real data sets that have been collected from the internet, but properly sanitized and anonymized... In a technical sense, this is easy. All you have to do is hook a computer up and start recording. But you end up picking up a lot of private information. We have been working on this with lawyers, the Electronic Privacy Information Center (EP...

Request for Help with OpenPacket.org

Image
Earlier this month I announced work on OpenPacket.org , a free site providing quality network traffic traces to researchers, analysts, and other members of the digital security community. We are looking for help in two areas: Open source content management systems (CMS) experience: We believe we will use a CMS to accept, moderate, and present traffic captures to users. We need help planning and deploying a CMS that will meet our needs. Open source database experience: We will use an open source database like MySQL or PostgreSQL, as compatible with the CMS we choose. We need help planning and deploying a database schema, and we will need guidance on configuring the database properly. Most of the OpenPacket.org crew has database experience as it relates to supporting intrusion detection sensors, but storing and retrieving the sorts of data we have in mind is probably outside our daily routine. We have ideas for additional OpenPacket.org functionality, but providing ways to accept, ...

OpenPacket.org Initial Announcement

Image
I would like to announce that I am working on a project called OpenPacket.org . The mission of OpenPacket.org is to provide quality network traffic traces to researchers, analysts, and other members of the digital security community. One of the most difficult problems facing researchers, analysts, and others is understanding traffic carried by networks. At present there is no central repository of traces from which a student of network traffic could draw samples. OpenPacket.org will provide one possible solution to this problem. Analysts looking for network traffic of a particular type will visit OpenPacket.org, query the OpenPacket.org Database for matching traces, and download those packets in their original format (e.g., Libpcap, etc.). The analyst will be able to process and analyze that traffic using tools of their choice, like Tcpdump, Snort, Ethereal, and so on. Analysts who collect their own traffic will be able to submit it to the OpenPacket.org database, assuming it is s...

1000th Post

Image
This is the 1000th TaoSecurity Blog post. Thankfully, after being broken for months, Blogger fixed the post tracking counter in time for me to notice this milestone. I started the blog on 8 January 2003 as a place to post word of new Amazon.com book reviews . I haven't read a new book since May, because I have been extremely busy launching my new company TaoSecurity . I plan to resume reading books very shortly, probably starting with Extreme Exploits . The blog has now evolved into a place where I record tips on using FreeBSD and other operating systems and applications. I also post thoughts on network security monitoring and related security topics. I constantly refer back to posts here to remember how I configured a program or what my thoughts were on a certain subject. I detest keeping bookmarks, so I try to store anything of value here. A bookmark has no context and says nothing about how or why I recorded it. In brief, this blog helps me keep a grip on developments ...