Posts

Showing posts with the label cisco

The Value of Branding and Simplicity to Certifications

Image
At the risk of stirring the cyber pot (item 3, specifically) I wanted to post a response to a great mailing list thread I've been following. A reader asked about the value of the CISSP certification. Within the context of the mailing list, several responders cited their thoughts on SANS certifications. Many mentioned why the CISSP tends to be so popular. I'd like to share my thoughts here. In my opinion, the primary reason the CISSP is so successful is that it is easy to understand it , which facilitates marketing it. It is exceptionally easy for a recruiter to search LinkedIn profiles, other databases, or resumes for the term "CISSP." If you encounter a person with the CISSP, you basically know what the person had to do to get the certification. Before continuing, answer this quick question: what are the following? 1) SSCP, 2) CAP, 3) CSSLP? Let me guess -- you didn't recognize any of them, just like I did? Now, let me see if you recognize any of the fo...

Cisco's Secure Routers Are Winning

Infonetics Research published a synopsis of a recent report they authored. I'd like to highlight a few points. Growth in the network security appliance and software market is expected to slow to the single-digits after 2007 as content security gateways and NAC products begin to infringe on network security product budgets. “The most important appliance category to watch over the next year is secure routers. Sales were up 25% in 2006 and this year will pass $1 billion in worldwide sales, representing a significant portion of the overall network security market..." Secure routers account for 29% of the total integrated security appliance market in 2006 and will continue to increase their share of the market through at least 2010... Cisco continues to lead the overall network security market, with 38% worldwide revenue share in 2006, posting growth in all network security market segments tracked by Infonetics Juniper and Check Point are tied for second, each with 9% worldwide ...

Earth to MARS

Image
Disclaimer: I'm going to single out a book by Cisco employees that talks about a Cisco product. I have no personal feelings about Cisco. I have friends there. I've done work for Cisco. Since I think Cisco is eventually going to own all network security functions in their switches , I may even work for Cisco one day. This post is for all product vendors who approach understanding and defending the network in the ways described here. Wherever you read "Cisco" feel free to add products that share the characteristics I outline below. Once again I found myself hanging in the sky last week. Trips to and from the West Coast gave me the opportunity to read Security Threat Mitigation and Response: Understanding Cisco Security MARS by Dale Tesch and Greg Abelar. This is mainly another Cisco marketing book, like Self-Defending Networks: The Next Generation of Network Security by Duane DeCapite. While I have a few thoughts on the book, I would much rather address the u...

Monitor Your Routers

Today I read this new Cisco advisory containing these words: Cisco routers and switches running Cisco IOS® or Cisco IOS XR software may be vulnerable to a remotely exploitable crafted IP option Denial of Service (DoS) attack. Exploitation of the vulnerability may potentially allow for arbitrary code execution. The vulnerability may be exploited after processing an Internet Control Message Protocol (ICMP) packet, Protocol Independent Multicast version 2 (PIMv2) packet, Pragmatic General Multicast (PGM) packet, or URL Rendezvous Directory (URD) packet containing a specific crafted IP option in the packet's IP header... A crafted packet addressed directly to a vulnerable device running Cisco IOS software may result in the device reloading or may allow execution of arbitrary code. This is the sort of "magic packet" that's an attacker's silver bullet. Send an ICMP echo with the right IP option to a router interface and whammo -- you could 0wn the router. Who would n...

Thoughts on Cisco Self-Defending Network Book

Image
I didn't exactly "read" Self-Defending Networks: The Next Generation of Network Security by Duane DeCapite. Therefore, I won't review the book at Amazon.com. I definitely didn't read a majority of the text, which is a personal requirement for a book review. However, I'd like to discuss the title here. The book has a ton of screen shots and is essentially a big marketing piece for Cisco's Self-Defending Network gear, which includes: Cisco Traffic Anomaly Detector for DDoS identification Cisco Guard for DDoS mitigation Adaptive Security Appliance for firewalling (including IPS) Incident Control System for malware containment with Trend Micro 802.1X for port-based security; note to Cisco: it's not "802.1x" Network Admission Control (NAC) with NAC Appliance or NAC Framework Cisco Security Agent (CSA) for host protection Cisco Security Manager Cisco Monitoring, Analysis and Response System (MARS) for alert management Why do I mentio...

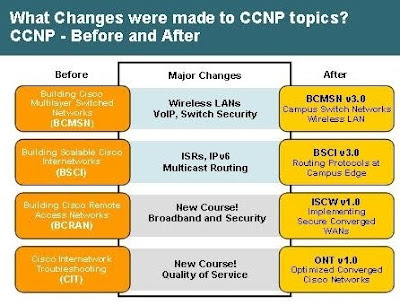
Notes from Cisco TV on CCNP

Image
I'm listening to the first episode of CCNP TV . It's not really TV, more like slides plus audio. I'm listening because I wanted to know about the CCNP changes mentioned earlier. The new material will all use Cisco IOS 12.4. I found this change interesting: assume I earn my CCNP; in the future, I can recertify using any Professional level exam, like one from CCSP. Mixing and matching of old and new exams will be allowed within the guidelines explained in these two press releases. Parts of this webcast were hilarious. Despite Cisco's drive into voice, none of the callers could communicate with the hosts. The caller who got closest to speaking should have been told "turn your radio down!" because the broadcast was on a 30 second-or-so delay. The host also asked two questions twice each, and the other panel members pretended like it didn't happen. I heard the terms "billion dollar marketplace" and "revenue opportunity" repeate...

CCNP Changes

If you're interested in earning the Cisco Certified Network Professional (CCNP) certification, you should read about changes in the cert. This TCPmag.com article is a nice summary. Basically Cisco removed some old material and added a lot more on security, wireless, and other modern topics. I would like to test for the CCNP before my CCNA expires in March 2008, but I'll wait until updated study books are available.

Brief Thoughts on Cisco AON

I received my copy of Cisco's Packet Magazine, Fourth Quarter 2005 recently. The new digital format for the magazine makes linking to anything impossible, but I found the relevant article as a .pdf. It describes the company's Application-Oriented Networking (AON) initiative. According to this story that quotes Cisco personnel, AON "is a network-embedded intelligent message routing system that integrates application message-level communication, visibility, and security into the fabric of the network." According to this document : Cisco AON is currently available in two products that integrate into Cisco switches and routers: Cisco Catalyst® 6500 Series AON module, which is primarily deployed in enterprise core or data centers Cisco 2600/2800/3700/3800 series AON module, which is primarily deployed at branch offices AON is part of Cisco's Intelligent Information Network project. From the article: "The Cisco AON module in the branch puts intelligent dec...

Measuring Bandwidth Utilization on Cisco Switch Ports

Yesterday I spoke at the third Net Optics Think Tank in Santa Clara, CA. During the event one of the Net Optics product managers asked me about measuring bandwidth utilization on switch ports. I did not have an answer for him... until I took a look at the latest Packet magazine. The Q305 (.pdf) edition features a tip from Aurelio DeSimone on p. 13 mentioning the show controllers utilization command. If anyone knows of a similar set of information via SNMP, please let me know via a comment here. Here is sample output: Switch> show controllers utilization Port Receive Utilization Transmit Utilization Fa0/1 0 0 Fa0/2 0 0 ...truncated... Total Ports : 12 Switch Receive Bandwidth Percentage Utilization : 0 Switch Transmit Bandwidth Percentage Utilization : 0 Switch Fabric Percentage Utilization : 0 This is just the sort of data I would like to see for SPAN ports. You can specify the SPAN port in your syntax ...

SecurityFocus SNMP Article

Image
Thanks to Simon Howard for pointing me toward a new article by Mati Aharoni and William M. Hidalgo titled Cisco SNMP configuration attack with a GRE tunnel . The article shows the dangers of not denying packets from the Internet using spoofed internal addresses. The article builds on Mark Wolfgang's Exploiting Cisco Routers: Part 1 , where an intruder uses an SNMP SET command to retrieve a router configuration file via TFTP. As Simon wrote in his email to me: "Applying an inbound ACL on the Ethernet0/0 interface denying any traffic from the 192.168.1.0 network would resolve this issue [in the article]." On a related note, I am looking forward to the second edition of Essential SNMP , pictured at left.

Thoughts on Cisco Packet Magazine

Image
I like to read Cisco's quarterly Packet magazine. It's free, and it provides insight into developments by the world's networking (and one day, security) juggernaut. While waiting for car maintenance this morning, I managed to read much of the Quarter 2 2005 issue , devoted to Self-Defending Networks . According to Cisco, they have been releasing Self-Defending Network components every few years. In 2000 they offered integrated security , followed by collaborative security in 2003. Now, in 2005, we have adaptive threat defense . The first term means security is part of Cisco products, such as routers and switches. The second term means these products should work together. Let's look closer at the third term, which Cisco claims will "protect every packet and every packet flow on a network." I was skeptical when I saw the cover text. The phrase "eliminating the source of attacks" and the sentence "network security grows adaptive, rea...

Cisco Connection Online Compromised?

Image
Thank you to Simon Howard for the tip. He and I were both unable to log into our Cisco Connection Online (CCO) accounts today. We received the warning above when authentication failed. The Register is now reporting Cisco portal password security compromised . The Cisco security page has this information: "Cisco Systems, Inc. was made aware of a vulnerability of a search tool on Cisco.com that could expose passwords for registered users. Registered users of Cisco.com consist of employees, customers, partners, and other third-party users. Cisco has since researched this issue and has taken the necessary steps to correct it. Cisco is taking precautionary measures to protect our registered Cisco.com users, including resetting registered user passwords." I wonder if Cisco has suffered a SQL injection breach? When I sent an email to have my account reset, I got this reply: "This is an automated reply ONLY to have your CCO p/w changed. DO NOT reply directly to this email...

More Resources on Ciscogate

The media is now calling the Lynn affair "Ciscogate." I'm using this term now because it's so much easier to Google. Multiple new articles provide good reading, including Exploit writers team up to target Cisco routers by Rob Lemos and Router Flaw Is a Ticking Bomb by Kim Zetter. The latter is an interview with Mike Lynn that has several choice quotes: "Cisco said, 'You guys are lying. It is impossible to execute shell code on Cisco IOS.' At that point (ISS) management was annoyed.... They were like, 'Mike, your new research project is Cisco IOS. Go find out how to exploit bugs on Cisco IOS so we can prove these people wrong...' [Cisco] also sent out an engineer ... who described himself as an IOS architect.... I was told he helped design parts of the source code.... And his jaw hit the ground. He was very impressed, he was just (saying), 'Wow, that's cool.' That was June 14th. WN [Wired News]: Cisco saw your Black Hat presentatio...

New Cisco Advisory and Statements

I guess we can wrap up the Cisco and ISS vs. Mike Lynn and Black Hat saga by mentioning the new Cisco security advisory released today: IPv6 Crafted Packet Vulnerability , which states: "(IOS®) Software is vulnerable to a Denial of Service (DoS) and potentially an arbitrary code execution attack from a specifically crafted IPv6 packet. The packet must be sent from a local network segment. Only devices that have been explicitly configured to process IPv6 traffic are affected. Upon successful exploitation, the device may reload or be open to further exploitation." Assuming these details are correct -- and who knows now? -- this is not an earth-shattering discovery. However, this may have been a sample vulnerability Mike demonstrated to explain his technique. He may have picked this vulnerability because he thought it would not affect much of the Internet, but he needed to let people know that his technique was already in use by malicious parties. Cisco's main security pa...

Cisco Releases IOS 12.4

I can't find any real press releases on this, but I noticed Cisco released IOS 12.4 this month. This is a Major Release that incorporates features developed in the IOS 12.3T line. Two product bulletins explain what's new in IOS 12.4, and an 84 slide .pdf presents similar information in PowerPoint format. I was surprised that the IOS Feature Navigator shows there is no support for the Secure Shell SSH Version 2 Server or Client for my Cisco 2651XM router in 12.4(1). Hopefully this will be added soon.

Researching Cisco Switch Backplane Statistics

While teaching at USENIX last week, I discussed SPAN ports . I mentioned that copying traffic to the SPAN port was less important than moving packets through the switch. One of the students asked if measuring the utilization of the switch backplane would reveal how well the switch was performing the SPAN function. Another student said there was a Simple Network Management Protocol Management Information Base (SNMP MIB) from which backplane statistics could be retrieved. I decided to research this issue as it affects using switches to collect traffic for network security monitoring. (Incidentally, Talisker offers SPAN port configuration advice for all sorts of switches.) One answer appears in the Cisco document How to Get Catalyst Switch Backplane Utilization Using SNMP . This sounds promising until we read "the information in this document is valid for Cisco Catalyst switches that run Catalyst code only." Since modern Cisco switches run IOS, we seem out of luck. Tha...

Cisco Routers Run Tcl

This morning I was reading The State of the Scripting Universe by Lynn Greiner. That article features interviews with leaders in the development communities for Perl, PHP, Python, Ruby, and Tcl. The article pointed me towards a reference titled Dynamic Languages — ready for the next challenges, by design by David Ascher. While reading this second article I was surprised by this statement: "Tcl is part of Cisco's IOS router operating system, and as such is included in all high-end Cisco routers and switches." What's that? Tcl on my router? A quick Google for "tcl cisco ios" revealed two helpful resources: Cisco IOS Scripting with Tcl by Cisco and TCL'ing Your Cisco Router by Peter J. Welcher. Cisco's document revealed that Tcl 8.3.4 was introduced in Cisco IOS 12.3(2)T. Sure enough, it's on my Cisco router: gill#sh ver Cisco IOS Software, C2600 Software (C2600-ADVSECURITYK9-M), Version 12.3(11)T3, RELEASE SOFTWARE (fc4) ...trucated......

Passed My CCNA Test

I just finished testing for my Cisco Certified Network Associate certification. I passed with a 973 out of 1000. The test was 90 minutes long and I finished with only 8 minutes to spare. I think I missed one question, maybe two. The exam was as tough as I expected, meaning it was not easy. I know it was difficult since I usually breeze through majority multiple-choice exams. (For example, I answered all 250 questions on the CISSP exam in 90 minutes, and walked out the door.) I cannot say enough about the CCNA class I took with Todd Lammle at GlobalNet Training . He was not kidding when he said students need to know everything he writes in his slides and says while teaching. I was amazed how much of my knowledge Cisco managed to test with a 55 question exam. Also, if I did not know Todd's block size method of IP subnetting, I do not think I would have finished the test in time. If you want to pass the CCNA, I recommend the following: 1. Take GlobalNet Training 's ...

Use FTP Instead of TFTP to Transfer IOS Images

Michael Lucas' book Cisco Routers for the Desperate saved me this evening. I was trying to update the flash image on my Cisco 2950T-24 switch via TFTP, and had this problem (twice, actually): gruden#copy tftp flash Address or name of remote host [192.168.2.7]? Source filename [c2950-i6k2l2q4-mz.121-22.EA3.bin]? Destination filename [c2950-i6k2l2q4-mz.121-22.EA3.bin]? Accessing tftp://192.168.2.7/c2950-i6k2l2q4-mz.121-22.EA3.bin... Loading c2950-i6k2l2q4-mz.121-22.EA3.bin from 192.168.2.7 (via Vlan1): !!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!! ...edited... !!!!!!!!!!!O!O!O!O!OO!OO!OO!OOOO %Error reading tftp://192.168.2.7/c2950-i6k2l2q4-mz.121-22.EA3.bin (Transfer aborted) Luckily the switch was not hosed at this point. I still had my command prompt and normal functionality. For some reason TFTP kept failing. The image stored on the TFTP server appeared good, since its MD5 hash matched that provided by Cisco. What to do? I remember...

Switch to Router-on-a-Stick Communication

In January I described how I configured my Cisco 2651XM router to pass traffic between two VLANs on my Cisco 2950T-24 switch. I never assigned an IP for management purposes to the switch, since I always reached it via console cable. Today I decided to try upgrading the switch IOS, but that required applying a management IP to the switch. My router had this configuration on the interface facing the switch: interface FastEthernet0/1 description Connection to gruden, Cisco switch no ip address duplex auto speed auto ! interface FastEthernet0/1.1 encapsulation dot1Q 10 ip address 10.10.10.1 255.255.255.0 ! interface FastEthernet0/1.2 encapsulation dot1Q 20 ip address 172.27.20.1 255.255.255.0 I assumed that if I assigned a management IP to my switch with either a 10.10.10.0/24 or 172.27.20.0/24 address, the switch would be able to speak to the router. I assigned 10.10.10.100/24 to the switch. Because switches do not receive IPs on individual ports, I applied the IP to VLAN 1: ...