Posts

Showing posts matching the search for engineering disasters

More Engineering Disasters

Image
I've written several times about engineering disasters here and elsewhere. Watching more man-made failures on The History Channel's "Engineering Disasters," I realized lessons learned the hard way by safety, mechanical, and structural engineers and operators can be applied to those practicing digital security. >In 1983, en route from Virginia to Massachusetts, the World War II-era bulk carrier SS Marine Electric sank in high seas. The almost forty year-old ship was ferrying 24,000 tons of coal and 34 Merchant Mariners, none of whom had survival suits to resist the February chill of the Atlantic. All but three died. The owner of the ship, Marine Transport Lines (MTL), blamed the crew and one of the survivors, Chief Mate Bob Cusick, for the disaster. Investigations of the wreck and a trial revealed the Marine Electric's coal hatch covers were in disrepair, as reported by Cusick prior to the disaster. Apparently the American Bureau of Shipping (ABS), an ins...
Engineering Disasters in Information Security Magazine

The December 2005 issue of Information Security magazine features an article I wrote titled History Lessons with the subtitle "Digital security could learn a lot from engineering's great disasters." It is based on this blog entry describing analog engineering disasters like the 1931 Yangze River damn failure, the 1944 Cleveland LNG tank fire, the 1981 Kansas City Hyatt Regency hotel walkway collapse, and the 1933 Atlanta Marriott parking lot sink hole. I am considering expanding this topic of digital security disasters to encompass a new book. I would like to take a historical and technical look at digital security failures on a case-by-case basis. Ideally the cases would be based on testimony from witnesses or participants wishing to (anonymously) share lessons with their colleagues. My concept is simple: when a bridge fails in the "analog" world, everyone knows about it. The disaster is visible, and engineers can analyze and learn from the event. The...

Further Thoughts on Engineering Disasters

My TiVo managed to save a few more episodes of Modern Marvels . You may remember I discussed engineering disasters last month. This episode of the show of the same title took a broader look at the problem. Three experts provided comments that resonated with me. First, Dr. Roger McCarthy of Exponent, Inc. offered the following story about problems with the Hubble Space Telescope. When Hubble was built on earth, engineers did not sufficiently address issues with the weight of the lens on Earth and deflections caused by gravity. When Hubble was put in orbit, the lens no longer deflected and as a result it was not the proper shape. Engineers on Earth had never tested the lens because they could not figure out a way to do it. So, they launched and hoped for the best -- only to encounter a disaster that required a $50 million orbital repair mission. Dr. McCarthy's comment was "A single test is worth a thousand expert opinions." This is an example of management by fa...

More on Engineering Disasters and Bird Flu

Here's another anecdote from the Engineering Disasters story I wrote about recently . In 1956 the cruise ship Andrea Doria was struck and sunk by the ocean liner Stockholm. At that time radar was still a fairly new innovation on sea vessels. Ship bridges were dimly lit, and the controls on radar systems were not illuminated. It is possible that the Stockholm radar operators misinterpreted the readings on their equipment, believing the Andrea Doria was 12 miles away when it was really 2 miles away. The ships literally turned towards one another on a collision course, based on faulty interpretation of radar contact in the dense fog. Catastrophe ensued. This disaster shows how humans can never be removed from the equation, and they are often at center stage when failures occur. The commentator on the show said a 10 cent ligh bulb illuminating the radar controls station could have shown the radar range was positioned in a setting different from that assumed by the operator. ...

Another Engineering Disaster

Does the following sound like any security project you may have worked? Executives decide to pursue a project with a timetable that is too aggressive, given the nature of the task. They appoint a manager with no technical or engineering experience to "lead" the project. He is a finance major who can neither create nor understand design documents. (This sounds like the news of MBA s being in vogue, as I reported earlier.) The project is hastily implemented using shoddy techniques and lowest-cost components. No serious testing is done. The only "testing" even tried does not stress the solution in any meaningful way -- it only "checks a box." Shortly after implementation, the solution shows signs of trouble. The project manager literally patches the holes and misdirects attention without addressing the underlying flaws. Catastrophe eventually ensues. What I've just described is the Boston Molasses Flood of 1919, best described by the Boston Society of ...

Engineering Disaster Lessons for Digital Security

I watched an episode of Modern Marvels on the History Channel this afternoon. It was Engineering Disasters 11 , one in a series of videos on engineering failures. A few thoughts came to mind while watching the show. I will provide commentary on each topic addressed by the episode. First discussed was the 1944 Cleveland liquified natural gas (LNG) fire. Engineers built a new LNG tank out of material that failed when exposed to cold, torching nearby homes and businesses when ignited. 128 people died. Engineers were not aware of the metal's failure properties, and absolutely no defensive measures were in place around the tank to protect civilian infrastructure. This disaster revealed the need to (1) implement plans and defenses to contain catastrophe, (2) monitor to detect problems and warn potential victims, and (3) thoroughly test designs against possible environmental conditions prior to implementation. These days LNG tanks are surrounded by berms capable of containing a...

Nisley on Failure Analysis

Since I'm not a professional software developer, the only reason I pay attention to Dr. Dobb's Journal is Ed Nisley. I cited him earlier in Ed Nisley on Professional Engineering and Insights from Dr. Dobb's . The latest issue features Failure Analysis , Ed's look at NASA 's documentation on mission failures. Ed writes: [R]eviewing your projects to discover what you do worst can pay off, if only by discouraging dumb stunts. What works for you also works for organizations, although few such reviews make it to the outside world. NASA, however, has done a remarkable job of analyzing its failures in public documents that can help the rest of us improve our techniques. Documenting digital disasters has been a theme of this blog, although my request for readers to share their stories went largely unheeded. This is why I would like to see (and maybe create/lead) a National Digital Security Board . Here are a few excerpts from Ed's article. I'm not going to s...

Brief Thought on Digital Security

I was asked to write an article for an upcoming issue of Information Security Magazine based on my Engineering Disasters blog post. I had the following thought after writing that article. When an engineering catastrophe befalls the "real" or "analog" world, it's often very visible. Failed bridges collapse, levees break, sink holes swallow buildings, and so on. If you look closely enough, prior to ultimate failure you see indications of pending doom. Cracks appear in concrete, materials swell or contract, groaning noises abound, etc. This is generally not the case in the digital world. It is possible for an enterprise to be completely owned by unauthorized parties, without any overt signs. If one knows where to look of course, indicators can be seen, and evidence of compromise can be gathered, analyzed, and escalated. This is the reason I advocate network security monitoring (NSM) and conducting traffic threat assessments (TTAs).

Management by Fact: Flight Data Recorder for Windows

Whenever I fly I use the time to read ;login: magazine from USENIX . Chad Verbowksi 's article The Secret Lives of Computers Exposed: Flight Data Recorder for Windows in the April 2007 issue was fascinating. (Nonmembers can't access it until next year -- sorry.) Chad describes FDR: Flight Data Recorder (FDR) collects events with virtually no system impact, achieves 350:1 compression (0.7 bytes per event), and analyzes a machine day of events in 3 seconds (10 million events per second) without a database. How is this possible, you ask? It turns out that computers tend to do highly repetitive tasks, which means that our event logs (along with nearly all other logs from Web servers, mail servers, and application traces) consist of highly repetitive activities. This is a comforting fact, because if they were truly doing 28 million distinct things every day it would be impossible for us to manage them. Ok, that's cool by itself. However, the insights gained from these lo...

Threat Deterrence, Mitigation, and Elimination

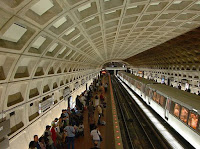
Image
A comment on my last post prompted me to answer here. My thesis is this: a significant portion, if not the majority, of security in the analog world is based on threat deterrence, mitigation, and elimination. Security in the analog world is not based on eliminating or applying countermeasures for vulnerabilities. A vulnerability-centric approach is too costly, inconvenient, and static to be effective. Consider the Metro subway in DC, pictured above. There are absolutely zero physical barriers between the platform and the trains. If evil attacker Evelyn were so inclined, she could easily push a waiting passenger off the platform into the path of an arriving train, maiming or killing the person instantly. Why does this not happen (regularly)? Evelyn is presumably a rational actor, and she is deterred by vigilante justice and the power of the legal system. If she killed a Metro passenger in the state of Virginia she would probably be executed herself, or at the very least spend...

Reference: TaoSecurity Research

I started publishing my thoughts and findings on digital security in 1999. I used to provide this information on my Web site, but since I don't keep that page up-to-date anymore, I decided to publish it here. 2015 and later: Please visit Academia.edu for Mr. Bejtlich's most recent research. 2014 and earlier: Seven Tips for Small Business Security , in the Huffington Post, 18 June 2014 Strategy, Not Speed: What Today's Digital Defenders Must Learn From Cybersecurity's Early Thinkers , for the Brookings Institution, 7 May 2014 What Federal Cyber Breach Notifications Really Mean for Business , for the Brookings Institution, 25 March 2014 Don't Underestimate Cyber Spies: How Virtual Espionage Can Lead to Actual Destruction in Foreign Affairs , 2 May 2013 Become a Hunter in the targeted-threat-centric Information Security Magzine, July-August 2011 (.pdf) Directions in Incident Detection and Response (.pdf) in the January/February 2011 issue of IEEE S...

Third of the Three Wise Men

Image
I just listened to my third of the Three Wise Men, Ross Anderson , courtesy of Gary McGraw's Silver Bullet Podcast . This is another must-heed. During the podcast Prof. Anderson mentioned the following: With respect to secure software development: As tools improve, we continue to "build bigger and better disasters." That echoes a theme in my previous posts. "If someone is going to call themselves a security engineer, then they have to learn how things fail." This means studying history and contemporary security disasters. That's an argument for my National Digital Security Board . Prof. Anderson mentioned potential compulsory registration for security professionals in the UK as a consequence of legislation requiring the registration of bouncers at clubs. Beware such an event here. Talk about unintended consequences. Finally, Prof. Anderson warned of vulnerabilities in Near Field Communication (NFC) technology. For goodness sake, can we slow down the ...

Does This Sound Familiar?

I read the following in the 2009 book Streetlights and Shadows: Searching for the Keys to Adaptive Decision Making by Gary Klein. It reminded me of the myriad ways operational information technology and security processes fail. This is a long excerpt, but it is compelling. == Begin == A commercial airliner isn't supposed to run out of fuel at 41,000 feet. There are too many safeguards, too many redundant systems, too many regulations and checklists. So when that happened to Captain Bob Pearson on July 23, 1983, flying a twin-engine Boeing 767 from Ottawa to Edmonton with 61 passengers, he didn't have any standard flight procedures to fall back on. First the fuel pumps for the left engine quit. Pearson could work around that problem by turning off the pumps, figuring that gravity would feed the engine. The computer showed that he had plenty of fuel for the flight. Then the left engine itself quit. Down to one engine, Pearson made the obvious decision to divert fr...