Posts

One Weird Trick for Reviewing Zeek Logs on the Command Line!

Are you a network security monitoring dinosaur like me? Do you prefer to inspect your Zeek logs using the command line instead of a Web-based SIEM? If yes, try this one weird trick! I store my Zeek logs in JSON format. Sometimes I like to view the output using jq. If I need to search directories of logs for a string, like a UID, I might* use something like zgrep with the following syntax: $ zgrep "CLkXf2CMo11hD8FQ5" 2020-08-16/* 2020-08-16/conn_20200816_06:00:00-07:00:00+0000.log.gz:{"_path":"conn","_system_name":"ds61","_write_ts":"2020-08-16T06:26:10.266225Z","_node":"worker-01","ts":"2020-08-16T06:26:01.485394Z","uid":"CLkXf2CMo11hD8FQ5","id.orig_h":"192.168.2.76","id.orig_p":53380,"id.resp_h":"196.216.2.24","id.resp_p":21,"proto":"tcp","service":"ftp",...

I Did Not Write This Book

Image
Fake Book  Someone published a "book" on Amazon and claimed that I wrote it! I had NOTHING to do with this. I am working with Amazon now to remove it, or at least remove my name. Stay away from this garbage! Update: Thankfully, within a day or so of this post, the true author of this work removed it from Amazon. It has not returned, at least as far as I have seen.

New Book! The Best of TaoSecurity Blog, Volume 1

Image
I'm very pleased to announce that I've published a new book! It's  The Best of TaoSecurity Blog, Volume 1: Milestones, Philosophy and Strategy, Risk, and Advice . It's available now in the Kindle Store , and if you're a member of Kindle Unlimited, it's currently free. I may also publish a print version. If you're interested, please tell me on Twitter . The book lists at 332 pages and is over 83,000 words. I've been working on it since last year, but I've used the time in isolation to carry the first volume over the finish line. The Amazon.com description says: Since 2003, cybersecurity author Richard Bejtlich has been writing posts on TaoSecurity Blog, a site with 15 million views since 2011. Now, after re-reading over 3,000 posts and approximately one million words, he has selected and republished the very best entries from 17 years of writing. In the first volume of the TaoSecurity Blog series, Bejtlich addresses milestones, phi...

If You Can't Patch Your Email Server, You Should Not Be Running It

Image
CVE-2020-0688 Scan Results, per Rapid7 tl;dr -- it's the title of the post: "If You Can't Patch Your Email Server, You Should Not Be Running It." I read a disturbing story today with the following news: "Starting March 24, Rapid7 used its Project Sonar internet-wide survey tool to discover all publicly-facing Exchange servers on the Internet and the numbers are grim. As they found, 'at least 357,629 (82.5%) of the 433,464 Exchange servers' are still vulnerable to attacks that would exploit the CVE-2020-0688 vulnerability. To make matters even worse, some of the servers that were tagged by Rapid7 as being safe against attacks might still be vulnerable given that 'the related Microsoft update wasn’t always updating the build number.' Furthermore, 'there are over 31,000 Exchange 2010 servers that have not been updated since 2012 ,' as the Rapid7 researchers observed. ' There are nearly 800 Exchange 2010 servers that have...

Seeing Book Shelves on Virtual Calls

Image
I have a confession... for me, the best part of virtual calls, or seeing any reporter or commentator working for home, is being able to check out their book shelves. I never use computer video, because I want to preserve the world's bandwidth. That means I don't share what my book shelves look like when I'm on a company call. Therefore, I thought I'd share my book shelves with the world. My big categories of books are martial arts, mixed/miscellaneous, cybersecurity and intelligence, and military and Civil War history. I've cataloged about 400 print books and almost 500 digital titles. Over the years I've leaned towards buying Kindle editions of any book that is mostly print, in order to reduce my footprint. For the last many years, my book shelving has consisted of three units, each with five shelves. Looking at the topic distribution, as of 2020 I have roughly 6 shelves for martial arts, 4 for mixed/miscellaneous, 3 for cybersecurity and intelligence, a...

Skill Levels in Digital Security

Image
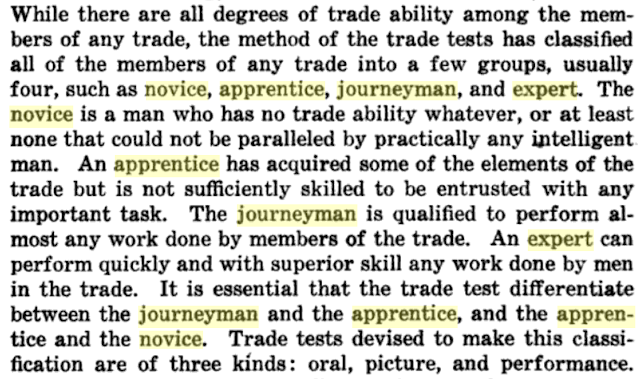
Two posts in one day? These are certainly unusual times. I was thinking about words to describe different skill levels in digital security. Rather than invent something, I decided to review terms that have established meaning. Thanks to Google Books I found this article in a 1922 edition of the Archives of Psychology that mentioned four key terms: The novice is a (person) who has no trade ability whatever, or at least none that could not be paralleled by practically any intelligent (person). An apprentice has acquired some of the elements of the trade but is not sufficiently skilled to be trusted with any important task. The journey(person) is qualified to perform almost any work done by members of the trade. An expert can perform quickly and with superior skill any work done by (people) in the trade. I believe these four categories can apply to some degree to the needs of the digital security profession. At GE-CIRT we had three levels -- event analyst, incident...

When You Should Blog and When You Should Tweet

Image
I saw my like-minded, friend-that-I've-never-met Andrew Thompson Tweet a poll , posted above. I was about to reply with the following Tweet: "If I'm struggling to figure out how to capture a thought in just 1 Tweet, that's a sign that a blog post might be appropriate. I only use a thread, and no more than 2, and hardly ever 3 (good Lord), when I know I've got nothing more to say. "1/10," "1/n," etc. are not for me." Then I realized I had something more to say, namely, other reasons blog posts are better than Tweets. For the briefest moment I considered adding a second Tweet, making, horror of horrors, a THREAD, and then I realized I would be breaking my own guidance. Here are three reasons to consider blogging over Tweeting. 1. If you find yourself trying to pack your thoughts into a 280 character limit, then you should write a blog post. You might have a good idea, and instead of expressing it properly, you're falling into...