Posts

Showing posts with the label kill chain

Five Thoughts from VADM Rogers Testimony
Image
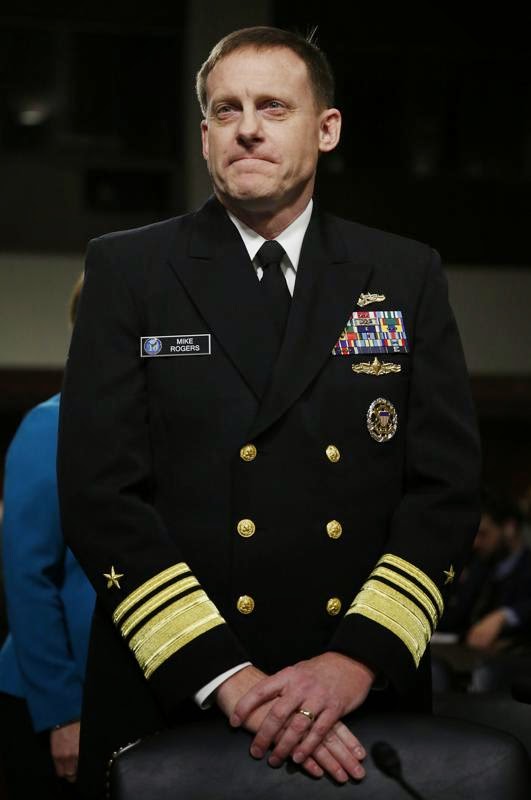
I had a chance to read  Advance Questions for Vice Admiral Michael S. Rogers, USN (pdf) this weekend. I wanted to share five thoughts based on excerpts from the VADM Rogers' answers to written questions posed by the Senate Armed Services Committee. 1. The Committee asked: Can deterrence be an effective strategy in the absence of reliable attribution? VADM Rogers responded: Yes, I believe there can be effective levels of deterrence despite the challenges of attribution. Attribution has improved, but is still not timely in many circumstances... Cyber presence, being forward deployed in cyberspace , and garnering the indications and warnings of our most likely adversaries can help (as we do with our forces dedicated to Defend the Nation). (emphasis added) I wonder if "cyber presence" and "being forward deployed in cyberspace" means having access to adversary systems? There's little doubt as to the source of an attack if you are resident on the sy...

Comparing IEDs and Digital Threats

Image
Two weeks ago Vago Muradian from This Week in Defense News interviewed Army Lt Gen Michael Barbero , commander of the Joint IED Defeat Organization. I was struck by the similarities between the problems his command handles regarding improvised explosive devices (IEDs) and those involving digital security professionals. In fact, you may be aware that papers and approaches like Intelligence-Driven Computer Network Defense Informed by Analysis of Adversary Campaigns and Intrusion Kill Chains by Eric M. Hutchins, Michael J. Cloppert, and Rohan M. Amin, Ph.D. were inspired by the desire to move "left of boom" regarding IEDs. In this post I will highlight elements from the interview which will likely resonate with those working digital security problems. The threat "shares information globally," and engages in an "arms race" with defenders, sometimes by "sitting in front of a computer" devising the latest tools and techniques. The adversary c...

Thoughts on "Cyber Weapons"

Image
With all the activity concerning Stuxnet, I've been thinking about "cyber weapons." You might recognize the image at left as coming from the venerable rootkit.com site operated by Greg Hoglund since 1999 (for real -- check out archive.org !) When Greg started that site I remember a lot of people complaining about cyber weapons and putting offensive tools in the wrong hands. Now with tools like Metasploit and Ronin , people are bound to worry about the same issues. It would be terrible to see valuable tools get painted with the same "ban the guns" prescriptions I expect to hear when Stuxnet becomes more popular in the media. So, in this post I'd like to share a few thoughts on differentiating security tools from cyber weapons (CWs). These are just my thoughts so I'd be interested in feedback. Some of them may be controversial and I could probably argue the opposite case for some of the items. Operators develop CWs privately. I don't think a ...

Mike Cloppert on Defining APT Campaigns

Image
Please stop what you're doing and read Mike Cloppert's latest post Security Intelligence: Defining APT Campaigns . Besides very clearly and concisely explaining how to think about APT activity, Mike includes some original Tufte-esque figures to demonstrate APT attribution and moving up the kill chain.

Attribution Is Not Just Malware Analysis

Image
In a recent Tweet I recommended reading Joe Stewart's insightful analysis of malware involved in Google v China . Joe's work is stellar as always, but I am reading more and more commentary that shows many people don't have the right frame of reference to understand this problem. In brief, too many people are focusing on the malware alone. This is probably due to the fact that the people making these comments have little to no experience with the broader problems caused by advanced persistent threat. It's enough for them to look at the malware and then move to the next sample, or devise their next exploit, and so on. Those of us responsible for defending an enterprise can't just look at the problem from a malware, or even a technical, perspective. I was reminded of this imperative when I read Waziristan: The Last Frontier in a recent Economist magazine. [I]t is tempting to think Waziristan has hardly changed since those colonial days... Mostly, [the Pakista...