Posts

Happy 16th Birthday TaoSecurity Blog

Image
Today, 8 January 2019, is TaoSecurity Blog's 16th birthday! This is also my 3,041st blog post. I wrote my first post on 8 January 2003 while working as an incident response consultant for Foundstone. Here are a few statistics on the blog. Blogger started providing statistics in May 2010, so these apply to roughly the past 9 years only. As of today, since May 2010 the blog has nearly 9.4 million all time page views, up from 7.7 million a year ago. Here are the most popular posts of the last 9 years, as of today: I'm blogging a bit more recently, with 22 posts in 2018 -- more than my total for 2016 and 2017 combined, but still not half as much as 2015, which saw 55 posts. Twitter continues to play a role in the way I communicate. Last year  @taosecurity  had nearly 49,000 followers with less than 18,000 Tweets. Today I have nearly 53,000 followers with 19,000 Tweets. My rule is generally this: if I start wondering how to fit an idea in 280 characters on Twitt...
Notes on Self-Publishing a Book

Image
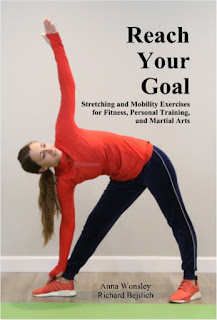
In this post I would like to share a few thoughts on self-publishing a book , in case anyone is considering that option. As I mentioned in my post on  burnout , one of my goals was to publish a book on a subject other than cyber security. A friend from my Krav Maga school, Anna Wonsley , learned that I had  published several books , and asked if we might collaborate on a book about stretching. The timing was right, so I agreed. I published my first book with Pearson and Addison-Wesley in 2004, and my last with No Starch in 2013. 14 years is an eternity in the publishing world, and even in the last 5 years the economics and structure of book publishing have changed quite a bit. To better understand the changes, I had dinner with one of the finest technical authors around, Michael W. Lucas . We met prior to my interest in this book, because I had wondered about publishing books on my own. MWL started in traditional publishing like me, but has since become a full-time ...

Managing Burnout

Image
This is not strictly an information security post, but the topic likely affects a decent proportion of my readership. Within the last few years I experienced a profound professional "burnout." I've privately mentioned this to colleagues in the industry, and heard similar stories or requests for advice on how to handle burnout. I want to share my story in the hopes that it helps others in the security scene, either by coping with existing burnout or preparing for a possible burnout. How did burnout manifest for me? It began with FireEye's acquisition of Mandiant, almost exactly five years ago. 2013 was a big year for Mandiant, starting with the APT1 report in early 2013 and concluding with the acquisition in December. The prospect of becoming part of a Silicon Valley software company initially seemed exciting, because we would presumably have greater resources to battle intruders. Soon, however, I found myself at odds with FireEye's culture and managerial...

The Origin of the Quote "There Are Two Types of Companies"

Image
While listening to a webcast this morning, I heard the speaker mention There are two types of companies: those who have been hacked, and those who don’t yet know they have been hacked. He credited Cisco CEO John Chambers but didn't provide any source. That didn't sound right to me. I could think of two possible antecedents. so I did some research. I confirmed my memory and would like to present what I found here. John Chambers did indeed offer the previous quote, in a January 2015 post for the World Economic Forum titled What does the Internet of Everything mean for security?  Unfortunately, neither Mr Chambers nor the person who likely wrote the article for him decided to credit the author of this quote. Before providing proper credit for this quote, we need to decide what the quote actually says. As noted in this October 2015 article by Frank Johnson titled Are there really only “two kinds of enterprises”? , there are really (at least) two versions of this quote:...

The Origin of the Term Indicators of Compromise (IOCs)

Image
I am an historian . I practice digital security, but I earned a bachelor's of science degree in history from the United States Air Force Academy. (1) Historians create products by analyzing artifacts, among which the most significant is the written word. In my last post , I talked about IOCs, or indicators of compromise. Do you know the origin of the term? I thought I did, but I wanted to rely on my historian's methodology to invalidate or confirm my understanding. I became aware of the term "indicator" as an element of indications and warning (I&W), when I attended Air Force Intelligence Officer's school in 1996-1997. I will return to this shortly, but I did not encounter the term "indicator" in a digital security context until I encountered the work of Kevin Mandia. In August 2001, shortly after its publication, I read Incident Response: Investigating Computer Crime , by Kevin Mandia, Chris Prosise, and Matt Pepe (Osborne/McGraw-Hill). I ...

Even More on Threat Hunting

Image
In response to my post More on Threat Hunting , Rob Lee asked : [D]o you consider detection through ID’ing/“matching” TTPs not hunting? To answer this question, we must begin by clarifying "TTPs." Most readers know TTPs to mean tactics, techniques and procedures, defined by David Bianco in his Pyramid of Pain post as: How the adversary goes about accomplishing their mission, from reconnaissance all the way through data exfiltration and at every step in between. In case you've forgotten David's pyramid, it looks like this. It's important to recognize that the pyramid consists of indicators of compromise (IOCs). David uses the term "indicator" in his original post, but his follow-up post from his time at Sqrrl makes this clear: There are a wide variety of IoCs ranging from basic file hashes to hacking Tactics, Techniques and Procedures (TTPs). Sqrrl Security Architect, David Bianco, uses a concept called the Pyramid of Pain to categorize...

More on Threat Hunting

Image
Earlier this week hellor00t asked via Twitter : Where would you place your security researchers/hunt team? I replied : For me, "hunt" is just a form of detection. I don't see the need to build a "hunt" team. IR teams detect intruders using two major modes: matching and hunting. Junior people spend more time matching. Senior people spend more time hunting. Both can and should do both functions. This inspired Rob Lee to blog a response, from which I extract his core argument: [Hunting] really isn’t, to me, about detecting threats... Hunting is a hypothesis-led approach to testing your environment for threats. The purpose, to me, is not in finding threats but in determining what gaps you have in your ability to detect and respond to them... In short, hunting, to me, is a way to assess your security (people, process, and technology) against threats while extending your automation footprint to better be prepared in the future. Or simply stated, it’s ...