Posts

How to Minimize Leaking
Image
I am hopeful that President Trump will not block release of the remaining classified documents addressing the 1963 assassination of President John F. Kennedy. I grew up a Roman Catholic in Massachusetts, so President Kennedy always fascinated me. The 1991 Oliver Stone movie JFK fueled several years of hobbyist research into the assassination. (It's unfortunate the movie was so loaded with fictional content!) On the 30th anniversary of JFK's death in 1993, I led a moment of silence from the balcony of the Air Force Academy chow hall during noon meal. While stationed at Goodfellow AFB in Texas, Mrs B and I visited Dealey Plaza in Dallas and the Sixth Floor Museum . Many years later, thanks to a 1992 law partially inspired by the Stone movie, the government has a chance to release the last classified assassination records. As a historian and former member of the intelligence community, I hope all of the documents become public. This would be a small but significant step towa...

Latest Book Inducted into Cybersecurity Canon

Image
Thursday evening Mrs B and I were pleased to attend an awards seminar for the Cybersecurity Canon . This is a project sponsored by Palo Alto Networks and led by Rick Howard. The goal is "identify a list of must-read books for all cybersecurity practitioners." Rick reviewed my fourth book The Practice of Network Security Monitoring in 2014 and someone nominated it for consideration in 2016. I was unaware earlier this year that my book was part of a 32-title "March Madness" style competition . My book won the five rounds, resulting in its conclusion in the 2017 inductee list! Thank you to all those that voted for my book. Ben Rothke awarded me the Canon trophy. Ben Rothke interviewed me prior to the induction ceremony. We discussed some current trends in security and some lessons from the book. I hope to see that interviewed published by Palo Alto Networks and/or the Cybersecurity canon project in the near future. In my acceptance speech I explained how ...

Five Reasons I Want China Running Its Own Software

Image
Periodically I read about efforts by China, or Russia, or North Korea, or other countries to replace American software with indigenous or semi-indigenous alternatives. I then reply via Twitter that I love the idea, with a short reason why. This post will list the top five reasons why I want China and other likely targets of American foreign intelligence collection to run their own software. 1. Many (most?) non-US software companies write lousy code.  The US is by no means perfect, but our developers and processes generally appear to be superior to foreign indigenous efforts. Cisco vs Huawei is a good example. Cisco has plenty of problems, but it has processes in place to manage them, plus secure code development practices. Lousy indigenous code means it is easier for American intelligence agencies to penetrate foreign targets. (An example of a foreign country that excels in writing code is Israel, but thankfully it is not the same sort of priority target like China, Russia, or ...

Cybersecurity Domains Mind Map

Image
Last month I retweeted an image labelled "The Map of Cybersecurity Domains (v1.0)". I liked the way this graphic divided "security" into various specialties. At the time I did not do any research to identify the originator of the graphic. Last night before my Brazilian Jiu-Jitsu class I heard some of the guys talking about certifications. They were all interested in "cybersecurity" but did not know how to break into the field. The domain image came to mind as I mentioned that I had some experience in the field. I also remembered an article Brian Krebs asked me to write titled " How to Break Into Security, Bejtlich Edition ," part of a series on that theme. I wrote: Providing advice on “getting started in digital security” is similar to providing advice on “getting started in medicine.” If you ask a neurosurgeon he or she may propose some sort of experiment with dead frog legs and batteries. If you ask a dermatologist you might get advice ...

Bejtlich Moves On

Image
Exactly six years ago today I announced that I was joining Mandiant to become the company's first CSO . Today is my last day at FireEye, the company that bought Mandiant at the very end of 2013. The highlights of my time at Mandiant involved two sets of responsibilities. First, as CSO, I enjoyed working with my small but superb security team, consisting of Doug Burks, Derek Coulsen, Dani Jackson, and Scott Runnels. They showed that " a small team of A+ players can run circles around a giant team of B and C players. " Second, as a company spokesperson, I survived the one-of-a-kind ride that was the APT1 report . I have to credit our intel and consulting teams for the content, and our marketing and government teams for keeping me pointed in the right direction during the weeks of craziness that ensued. At FireEye I transitioned to a strategist role because I was spending so much time talking to legislators and administration officials. I enjoyed working with anoth...

The Missing Trends in M-Trends 2017

Image
FireEye released the 2017 edition of the Mandiant M-Trends report yesterday. I've been a fan of this report since the 2010 edition , before I worked at the company. Curiously for a report with the name "trends" in the title, this and all other editions do not publish the sorts of yearly trends I would expect. This post will address that limitation. The report is most famous for its "dwell time" metric, which is the median (not average, or "mean")  number of days an intruder spends inside a target company until he is discovered. Each report lists the statistic for the year in consideration, and compares it to the previous year. For example, the 2017 report, covering incidents from 2016, notes the dwell time has dropped from 146 days in 2015, to 99 days in 2016. The second most interesting metric (for me) is the split between internal and external notification. Internal notification means that the target organization found the intrusion on its...

The Origin of Threat Hunting

Image
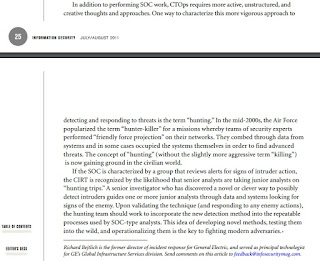
2011 Article "Become a Hunter" The term "threat hunting" has been popular with marketers from security companies for about five years. Yesterday Anton Chuvakin asked about the origin of the term. I appear to have written the first article describing threat hunting in any meaningful way. It was published in the July-August 2011 issue of Information Security Magazine and was called "Become a Hunter." I wrote it in the spring of 2011, when I was director of incident response for GE-CIRT. Relevant excerpts include: "To best counter targeted attacks, one must conduct counter-threat operations (CTOps). In other words, defenders must actively hunt intruders in their enterprise . These intruders can take the form of external threats who maintain persistence or internal threats who abuse their privileges. Rather than hoping defenses will repel invaders, or that breaches will be caught by passive alerting mechanisms, CTOps practitioners recognize that ...