Posts

Why Collect Full Content Data?
Image
I recently received the following via email: I am writing a SANS Gold paper on a custom full packet capture system using Linux and tcpdump. It is for the GSEC Certification, so my intent is to cover the reasons why to do full packet capture and the basic set up of a system (information that wasn't readily available when setting my system up)... I am already referencing The Tao of Network Security Monitoring . These are the questions that I came up with based on questions other peers have asked me... Here are the questions, followed by my answers. Most of this is covered in my previous books and blog posts, but for the sake of brevity I'll try posting short, stand-alone responses. As an information security analyst in today's threat landscape why would I want to do full packet capture in my environment? What value does have? Full content data or capturing full packets provides the most flexibility and granularity when analyzing network-centric data. Unlike vario...

Spectrum of State Responsibility

Image
"Attribution" for digital attacks and incidents is a hot topic right now. I wanted to point readers to this great paper by Jason Healey at the Atlantic Council titled Beyond Attribution: Seeking National Responsibility in Cyberspace . ACUS published the report in February, but I'm not hearing anyone using the terms described therein. Probably my favorite aspect of the paper is the chart pictured at left. It offers a taxonomy for describing state involvement in digital attacks, ranging from "state-prohibited" to "state-integrated." I recommend using the chart and ideas in the paper as a starting point the next time you have a debate over digital attribution. Tweet

Recommended: The Great Courses "Art of War" Class

Image
I recently purchased and listened to an audio course titled The Art of War (TAOW) by Prof Andrew R. Wilson and published by The Great Courses . From the first few minutes I knew this series of six 30 minute lessons was going to be great. For example, did you know that "Sun Tzu" didn't write "The Art of War?" An anonymous author wrote the book in the 4th century BC, based on Sun Tzu's lessons from his time in the 6th century BC. Also, "The Art of War" isn't even the name of the book! It's actually "Master Sun's Military Method." Furthermore, the use of the term "Master" is significant as it was a term not usually associated with generals. I especially like two aspects of the course. First, the lecturer, paraphrasing his own words, didn't choose to simply peruse TAOW looking for trite phrases. He equates that approach with telling a stock broker to "buy low, sell high." Instead, Prof Wilson is more c...

Commander's Reading List

Image
Last month a squadron commander asked me to recommend books for his commander's reading list. After some reflection I offer the following. I've divided the list into two sections: technical and nontechnical. My hope for the technical books is to share a little bit of technical insight with the commander's intended audience, while not overwhelming them. The plan for the nontechnical items is to share some perspective on history, policy, and contemporary problems. The list is in no particular order. Nontechnical books: America the Vulnerable by Joel Brenner Cyber War by Richard Clarke and Robert Knake Crypto by Steven Levy Geekonomics by David Rice Security Metrics by Andrew Jaquith The Victorian Internet by Tom Standage The Cuckoo's Egg by Cliff Stoll Tiger Trap by David Wise Technical books: Software Security by Gary McGraw The Art of Computer Virus Research and Defense by Peter Szor Real Digital Forensics by Keith Jones, Curtis Rose, and Ric...

Do Devs Care About Java (In)Security?

Image
In September InformationWeek published an article titled Java Still Not Safe, Security Experts Say . From that article by Matthew J. Schwartz: Is Java 7 currently safe to use? Last week, Oracle released emergency updates to fix zero-day vulnerabilities in Java 7 and Java 6. But in the case of the Java 7 fix, the new version allows an existing flaw--spotted by security researchers and disclosed to Oracle earlier this year--to be exploited to bypass the Java sandbox. In other words, while fixing some flaws, Oracle opened the door to another one. In light of that situation, multiple security experts said that businesses should continue to temporarily disable all Java use, whenever possible. "There are still not-yet-addressed, serious security issues that affect the most recent version of Java 7," said Adam Gowdiak, CEO and founder of Poland-based Security Explorations, which initially disclosed the exploited vulnerabilities to Oracle in April. "In that context, disab...

Review of Super Scratch Programming Adventure! Posted

Image
Amazon.com just posted a joint review by myself and my daughter of No Starch's new book Super Scratch Programming Adventure! . From the five star review : I asked my almost-8-year-old to share her thoughts on Super Scratch Programming Adventure! She chose five stars and wrote the following: "I think it's a very great book. I love the storyline, but my main concern is that I could not find a trace of the Super Scratch folder. How hard is it to draw the Mona Lisa? I have Scratch version 1.4, and I found it difficult drawing Le Louvre. On the flip side, I learned a lot. Who knew you could make Scratchy move with 1) arrow keys and 2) a medium sized Script? I enjoyed watching the Magic Star Web change colors. Overall, I think it's a very great book, and I highly recommend it to anyone who is interested in programming." I agree that this is a great book. My daughter wanted to learn how to program a video game, and I thought it would be a lot more difficult. Sho...

Washington National Guard: Model for Cyber Defense?

Image
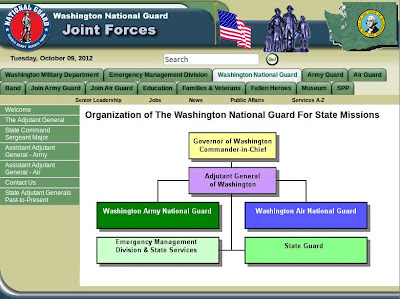
My friend Russ McRee pointed me to an article recently: WA National Guard focusing on cyber security . From the article: The Washington National Guard is leveraging a decade of investment in cyber security at Camp Murray in Lakewood into projects that could protect state and local governments, utilities and private industry from network attacks. The aim is to bring to the digital world the kind of disaster response the National Guard already lends to fighting wildfires and floods, said Lt. Col. Gent Welsh of the Washington Air National Guard. “Just as ‘Business X’ needs the National Guard to come in and fill sand bags, ‘Business X’ might need to call the National Guard if it’s overwhelmed on the cyber side,” Welsh said. The new task plays to a growing strength in the state’s National Guard, which draws on employees from companies including Microsoft and Amazon to provide special expertise in its network warfare units. I first learned of this initiative when Russ Tweeted abou...