Posts

Review of Super Scratch Programming Adventure! Posted

Image
Amazon.com just posted a joint review by myself and my daughter of No Starch's new book Super Scratch Programming Adventure! . From the five star review : I asked my almost-8-year-old to share her thoughts on Super Scratch Programming Adventure! She chose five stars and wrote the following: "I think it's a very great book. I love the storyline, but my main concern is that I could not find a trace of the Super Scratch folder. How hard is it to draw the Mona Lisa? I have Scratch version 1.4, and I found it difficult drawing Le Louvre. On the flip side, I learned a lot. Who knew you could make Scratchy move with 1) arrow keys and 2) a medium sized Script? I enjoyed watching the Magic Star Web change colors. Overall, I think it's a very great book, and I highly recommend it to anyone who is interested in programming." I agree that this is a great book. My daughter wanted to learn how to program a video game, and I thought it would be a lot more difficult. Sho...
Washington National Guard: Model for Cyber Defense?

Image
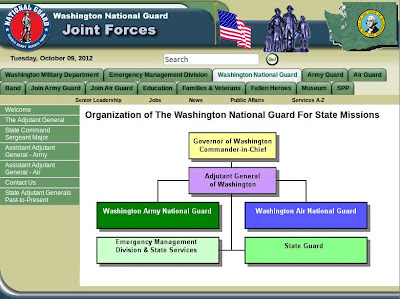
My friend Russ McRee pointed me to an article recently: WA National Guard focusing on cyber security . From the article: The Washington National Guard is leveraging a decade of investment in cyber security at Camp Murray in Lakewood into projects that could protect state and local governments, utilities and private industry from network attacks. The aim is to bring to the digital world the kind of disaster response the National Guard already lends to fighting wildfires and floods, said Lt. Col. Gent Welsh of the Washington Air National Guard. “Just as ‘Business X’ needs the National Guard to come in and fill sand bags, ‘Business X’ might need to call the National Guard if it’s overwhelmed on the cyber side,” Welsh said. The new task plays to a growing strength in the state’s National Guard, which draws on employees from companies including Microsoft and Amazon to provide special expertise in its network warfare units. I first learned of this initiative when Russ Tweeted abou...

Inside Saudi Aramco with 60 Minutes

Image
I just watched a recent episode of 60 Minutes on CNBC and enjoyed the segment on oil production in Saudi Arabia. It featured a story from late 2008 on Saudi Aramco. You may recall this name from recent news, namely data destruction affecting 30,000 computers . A recent Reuters article said the following: Saudi Aramco has said that only office PCs running Microsoft Windows were damaged. Its oil exploration, production, export, sales and database systems all remained intact as they ran on isolated and heavily protected systems. "All our core operations continued smoothly," CEO Khalid Al-Falih told Saudi government and business officials at a security workshop on Wednesday. "Not a single drop of oil was lost. No critical service or business transaction was directly impacted by the virus." It is standard industry practice to shield plant operating networks from hackers by running them on separate operating systems that are protected from the Internet. While wat...

Netanyahu Channels Tufte at United Nations

Image
This is not a political blog, and I don't intend for this to be a political post. I recently watched Israeli Prime Minster Benjamin Netanyahu's speech to the United Nations on Thursday. I watched it because I am worried about Iran's nuclear weapons program and the Iranian security situation, to be sure. However, what really intrigued me was the red line he actually drew on a diagram, in front of the United Nations. In the video I linked, it takes place at approximately the 26 minute mark. The screen capture at left shows this event. The reason this caught my attention was that it reminded me of the Best Single Day Class Ever , taught by Edward Tufte. I attended his class in 2008 and continue to recommend it. I've since blogged about Tufte on several occasions. Netanyahu's action, to me, seems like pure Tufte. The primary goal of his speech was to tell Iran, and the world, that Israel is setting a "red line" involving Iran's nuclear weapons pr...

Celebrate Packt Publishing's 1000th Title

Image
I'm pleased to announce a special event involving Packt Publishing . The company told me, as a way to celebrate their 1000th title, that those who have registered at https://www.packtpub.com/login by 30 September will receive one free e-book. To help you make your choice, Packt is also opening its online library for a week for free to members. I'm interested in two recent titles: Metasploit Penetration Testing Cookbook by Abhinav Singh Advanced Penetration Testing for Highly-Secured Environments by Lee Allen In a few months a third book will arrive: BackTrack 5 Cookbook At this point I don't have personal experience with any of these titles, but I plan to take a look. Thank you Packt for sharing part of your library with us! Tweet

Top Ten Ways to Stir the Cyber Pot

Image
I spent a few minutes just now thinking about the digital security issues that people periodically raise on their blogs, or on Twitter, or at conferences. We constantly argue about some of these topics. I don't think we'll ever resolve any of them. If you want to start a debate/argument/flamewar in security, pick any of the following. "Full disclosure" vs "responsible disclosure" vs whatever else Threat intelligence sharing Value of security certifications Exploit sales Advanced-ness, Persistence-ness, Threat-ness, Chinese-ness of APT Reality of "cyberwar" "Builders vs Breakers" "Security is an engineering problem," i.e., "building a new Internet is the answer." "Return on security investment" Security by mandate or legislation or regulation Did I miss any subjects people raise to "stir the cyber pot?" Tweet

Unrealistic "Security Advice"

Image
I just read a blog post (no need to direct traffic there with a link) that included the following content: This week, I had the opportunity to interview the hacking teams that used zero-day vulnerabilities and clever exploitation techniques to compromise fully patched iPhone 4S and Android 4.0.4 (Samsung S3) and the big message from these hackers was simple: Do not use your mobile device for *anything* of value, especially for work e-mail or the transfer of sensitive business documents. For many, this is not practical advice. After all, your mobile device is seen as an extension of the computer and there is a legitimate need to access work e-mail on iPhone/iPad, Android and BlackBerry smart phones. However, whether you are a businessman, a celebrity or the average consumer, it's important to start wrapping your mind around the idea of separating work from play on mobile devices. This author is well-meaning, but he completely misses the bigger picture. Against a sufficiently...